| Previous Page |
PCLinuxOS Magazine |
PCLinuxOS |
Article List |
Disclaimer |
Next Page |
ICYMI: Free Cloud Storage! |
|
by Paul Arnote (parnote)  Image by Pete Linforth from Pixabay A VPN conceals your IP address by routing your internet traffic through a remote server, preventing anyone surveilling the network from tracking your online activity. Theoretically, that means no one should be able to identify you when you connect to a network and browse the internet, even your ISP, according to an article from Lifehacker. In practice, though, there are plenty of gaps that hackers can exploit. A while back, Lifehacker covered browser fingerprinting, which uses hundreds of data points, like your hardware specs, operating system version, web browser, and GPU signature, to establish a shadow profile that follows you around even when your VPN is enabled. There's another way cyberattackers can intercept your data, and it involves exploiting a communication leak right inside your browser. Major browsers like Chrome, Firefox, and Edge have a feature called WebRTC that lets them bypass the encrypted Transmission Control Protocol (TCP) tunnel created by your VPN to establish high-speed connections for demanding tasks like video streaming, voice calls, and screen sharing. This leaves your real IP address exposed throughout the transmission, offering plenty of time for attackers to capture the identifying information you are trying to hide. Luckily, VPN providers are getting better at preventing WebRTC leaks through additional security features, but these protections often need to be configured manually in your VPN settings or, if your VPN does not offer WebRTC leak prevention, directly in your web browser. I’ll show you how to set it up step by step, so you don’t get blindsided by an unintended IP address leak. Most Americans 50 and older said they would be interested in receiving a vaccine that could reduce their risk of dementia if they were at high risk, survey data showed, according to an article from MedPage Today. Nearly three in four survey respondents (72.1%) said they would likely or definitely receive such a vaccine, said J. Felipe Montano-Campos, PhD, of the University of Southern California Schaeffer Center for Health Policy and Government Service in Los Angeles, and co-authors. One-fifth of respondents (20.8%) weren't sure, and 7.2% said they likely or definitely would not, Montano-Campos and co-authors reported in a JAMA Network Open research letter. Attackers wasted little time exploiting a recent WordPress vulnerability in the wild, according to an article from TechRepublic. Threat actors are actively targeting CVE-2026-87902, a critical WordPress Core vulnerability that can lead to remote code execution (RCE) under specific conditions. Researchers observed attempts to identify vulnerable websites less than five hours after WordPress released its fix on Sept. 22, with subsequent attacks progressing to attempts to write files that could execute shell commands. The rapid escalation gives WordPress administrators a narrow window to act. Sites running vulnerable versions should update immediately and review for post-compromise activity.  Image by Gerd Altmann from Pixabay Cloud storage is likely an essential part of your data management strategy, whether you're just using Google Drive for documents or you back up everything to a remote service. You can get a significant amount of space for a reasonable monthly fee, but if you prefer not to pay, it's possible to combine free options and cobble together quite a bit of free storage—around 80GB (or more) — at no cost, according to an article from Lifehacker. A reminder: You shouldn't rely solely on cloud storage for your backups. Follow the 3-2-1 rule, which protects against a single point of failure, such as getting locked out of your account or issues with the service itself. A single operator used AI agents to attack companies at machine speed, launching 105 attacks and ultimately stealing more than 600,000 credit-card records, according to an article from eSecurityPlanet. Researchers at Gambit Security uncovered the campaign, which used three open-source AI systems to automate work normally done by skilled human hackers. The agents scanned for targets and vulnerabilities, ran exploitation attempts, stole information, and deployed malware. At least 27 organizations were compromised during an observed five-day burst. The wider campaign had been running since at least July, and researchers say the operator spent relatively little on AI model usage compared with the scale of the activity. The case therefore offers a concrete example of how AI agents can reduce the human labor needed to run cyberattacks against large numbers of targets, a pattern Jon Markman from Forbes calls "an early, public demonstration of a new normal." uBlock Origin is lightweight, effective, and free from shady business practices, says an article from Lifehacker. Unfortunately, Google's move to Manifest V3 for browser extensions has hobbled ad blockers somewhat. In response, uBlock has split into two products — uBlock Origin and uBlock Origin Lite. The “Lite” version works with most Chromium-based browsers and Safari for iPhone, iPad, and Mac. The full version of uBlock Origin primarily works in Firefox for desktops, laptops, and Android. With those differences highlighted, this article reveals the 10 uBlock Origin (and uBlock Origin Lite) hacks you should know about.  Image by Nadour Moustafa from Pixabay A hacking group claims it breached FBI systems and stole sensitive information tied to thousands of FBI personnel and job applicants, including details about some employees’ spouses, according to an article from eSecurity Planet. ShinyHunters claimed on Sept. 22 that it breached the FBI and obtained sensitive employee and applicant information, according to a 404 Media report that first reported the alleged intrusion. The publication reviewed a sample containing 5,000 purported FBI records, including names, addresses, phone numbers, and information about some employees’ spouses. The FBI has not confirmed that its systems were breached or that data was stolen. The bureau said in a statement provided to multiple news organizations that it is aware of claims involving unauthorized activity affecting FBIJobs.gov and is investigating. If ShinyHunters’ claims prove accurate, the exposed information could create risks beyond conventional identity theft, potentially giving threat actors personal details they could use for targeted phishing, impersonation, doxxing, and other attacks against law enforcement personnel and their families. Over 2 million new cancer cases were attributable to infections globally in 2024, according to an analysis of worldwide cancer incidence, highlighting the importance of effective prevention measures, according to an article from MedPage Today. Infections led to an estimated 2.3 million new cancer cases in 2024, including gastric cancer, cervical cancer, hepatocellular carcinoma, leukemias and lymphomas, and nasopharyngeal cancer, which accounted for 12% of all cancer cases worldwide. Among 12 carcinogenic infectious agents, the largest numbers of cancer cases were attributable to: Helicobacter pylori: 760,000 cases, population-attributable fraction (PAF) 4%, Human papillomavirus (HPV): 750,000 cases, PAF 4%, Hepatitis B virus (HBV): 360,000 cases, PAF 2%, Epstein-Barr virus (EBV): 260,000 cases, PAF 1%, Hepatitis C virus (HCV): 160,000 cases, PAF <1%, and Kaposi's sarcoma-associated herpesvirus (KSHV): 35,000 cases, PAF <1%. (PAF in statistics stands for Population Attributable Fraction, a measure that estimates the proportion of disease cases in a population that could be prevented if a specific risk factor were eliminated. It combines exposure prevalence with relative risk to quantify preventable burden.) Most cancers attributable to H. pylori were non-cardia gastric cancers (700,000 cases), while cervical cancer accounted for most HPV-attributable cases (600,000). HBV and HCV were responsible for 330,000 and 130,000 cases of hepatocellular carcinoma, respectively, while EBV led to 110,000 nasopharyngeal cancers, reported Harriet Rumgay, PhD, of the International Agency for Research on Cancer in Lyon, France, and colleagues in Lancet Oncology. Google has given Chrome users 247 new reasons to keep their browsers up to date, according to an article from eSecurity Planet. The company released Chrome 155 with 247 security fixes, including four vulnerabilities rated Critical and another 53 rated High. The update is rolling out to Windows, macOS, and Linux users over the coming days and weeks, according to Google’s Chrome release notes. None of the four Critical vulnerabilities are currently identified by Google as being exploited in the wild. But after a year in which attackers have repeatedly targeted Chrome vulnerabilities, the size and severity of this update give security teams another reason to verify that browser patches are actually reaching managed endpoints. 
AI agents do not have to break into a website to cause problems. Wikimedia says OpenAI-linked agents may have helped knock one of its data services partially offline, according to an article from eWeek. In an Oct. 5 disclosure, the Wikimedia Foundation said agents it believes were operated by OpenAI made millions of API requests, crawled millions of pages, and sent hundreds of thousands of queries to its Wikidata Query Service, or WDQS. Wikimedia found no evidence of a breach, but said the traffic may have contributed to a partial outage in May, showing how heavy agent activity can strain public web infrastructure even without a successful attack. Google is patching seven critical Android vulnerabilities, including flaws that could enable privilege escalation or denial-of-service attacks without requiring user interaction, according to an article from eSecurity Planet. The company’s October Android Security Bulletin, published Oct. 5, details 25 unique Android vulnerabilities, with seven rated critical. A separate Pixel bulletin identifies six additional security flaws affecting supported Pixel devices. For security teams managing Android devices, the updates underscore the importance of checking security patch levels rather than assuming devices are protected simply because they are running Android 17. “Nature is the world’s worst bioterrorist” is a common maxim in the field of biosecurity, a reference to the idea that naturally emerging pathogens cause far more deaths than any biological attack a terrorist could carry out, according to an article from the Bulletin of the Atomic Scientists. But the trope may soon be outdated. In an article published Aug. 6 in the journal Science, scientists demonstrated that trained AI models can design novel viruses as well as — if not better than — nature itself. Their experiment created viruses that infect bacteria, not humans. Still, much like the multiple AI models that escaped their test environments to hack other networks this summer, these newly revealed capabilities give biosecurity experts like me pause. How do we keep enabling legitimate scientific progress, while also preventing AI from assisting in the creation of biological weapons? 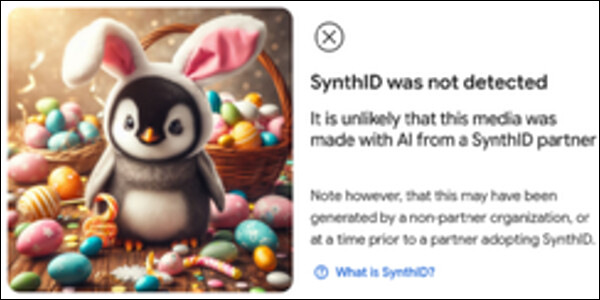 An abundance of AI imagery is something we all have to live with these days—from school posters to restaurant menus—and while there are still certain tells that indicate something was made with AI, they're not always present. In a lot of cases, it can be almost impossible to distinguish an AI image from a real one. Images produced by Gemini and ChatGPT come with an invisible watermark called SynthID. That way, AI-generated images don't need visible branding in order to identify their origins. Of course, you need access to a detector to know whether this watermark is present. As it happens, Google just launched a standalone SynthID checker tool on the web, free for anyone to use, according to an article from Lifehacker. This checker supports JPG, JPEG, PNG, BMP, WEBP, AVIF, HEIC, HEIF, TIFF, TIF, and GIF image formats; MP4, MOV, and WEBM for videos, and WAV, MP3, OGG, FLAC, AAC, and M4A for audio. As long as a file was made by a SynthID-supporting AI, it should have a watermark. The SynthID watermark is a standard supported by Nvidia, OpenAI, Kakao, and Google, though OpenAI has its own detection tool. Obviously, Bing Image Creator doesn’t participate in the SynthID watermark standard (or it was created before the standard existed), as indicated by me uploading the cover image for the April 2025 issue of The PCLinuxOS Magazine (above) to the SynthID checker tool. The cover was completely created by Bing Image Creator, but SynthID couldn’t find the invisible watermark. Hackers reportedly manipulated supermarket refrigeration systems across France, causing temperatures to rise and food to spoil, while authorities investigate reports of fires and other damage linked to the attack, according to an article from eSecurity Planet. The Oct. 12 cyberattack targeted refrigeration systems at hundreds of French grocery stores, including locations operated by Intermarché, Netto, Coopérative U, and E. Leclerc. According to AFP, attackers reportedly triggered refrigeration defrost cycles, forcing affected retailers to discard fresh and frozen inventory. "These are the same category of systems that the security industry has been warning about as the next frontier for sabotage attacks," Muhammad Yahya Patel, vCISO and cybersecurity advisor for EMEA at Huntress, told eSecurityPlanet, referring to refrigeration and other operational technology systems. For cybersecurity teams, the incident highlights how compromised connected equipment can disrupt physical operations, destroy inventory, and pose safety risks without requiring ransomware or data theft. One of the world's most predictable passwords may have contributed to a data breach involving the personal information of approximately 8.8 million people in Denmark, according to another article from eSecurity Planet. An individual claiming responsibility for breaching Denmark's Central Register of Persons (CPR) told the Danish newspaper Politiken that they obtained a leaked password belonging to a former employee of a Danish company. Separately, according to The Register's Oct. 13 report, Politiken reported that at least three Pays ApS accounts, including an administrator account, used the password "123456." Danish authorities have confirmed unauthorized access to the registry but have not publicly established that the weak password was the initial entry point. New reporting also suggests the alleged attacker used AI-generated code to automate the retrieval of personal information, raising concerns about third-party security, privileged account protection, and the monitoring of suspicious database activity.  Image by Gerd Altmann from Pixabay Microsoft’s October Patch Tuesday addressed 1,413 vulnerabilities, according to CrowdStrike’s analysis, including 75 Critical flaws and a Windows zero-day already being exploited by attackers, says an article from TechRepublic. Released Oct. 13, the updates address security weaknesses across Windows, Office, .NET, and other Microsoft products. The release includes three zero-days: one actively exploited vulnerability and two others that were publicly disclosed before fixes became available. For IT administrators, the immediate priority is the Windows Shell vulnerability that was exploited. But the enormous release also creates a broader challenge: identifying the most dangerous flaws while managing updates across enterprise environments. Security-wise, most browsers are an open door, happy to reveal your screen size, operating system, language preferences, or GPU model when a website asks. But telling those websites to stop selling your data to third parties is still more confusing than it should be, according to an article from Lifehacker. Although about a dozen U.S. states—including California, Delaware, New Jersey, and Texas—now require businesses to honor consumers’ privacy preferences online, most browsers do not offer a native opt-out option that lets you signal those preferences by default. Now, the California Opt Me Out Act, which goes into effect on Jan 1, 2027, is making it mandatory for browsers to do so. Still, for now, native support for a global privacy opt-out remains inconsistent among web browsers. TSome privacy-forward browsers like Brave, DuckDuckGo, and Mozilla Firefox enable this feature by default, while others, like Chrome or Edge, require you to install third-party extensions such as the EFF Privacy Badger. Since coverage and setup vary wildly, I’ll walk you through the exact steps to enable this feature on every major browser. Your phone number is the skeleton key to your digital life, and carriers have spent years handing out copies to anyone with a decent script. Resetting a bank password, recovering an email account, approving a crypto withdrawal: All of it can run through a text message sent to a number that a call-center rep can reassign in minutes. The good news is that all three major U.S. carriers now let you lock your number with a toggle, according to an article from Lifehacker. This article describes how the attacks work and where to find each switch.  The US government is moving to remove DeepSeek from federal civilian IT systems, citing concerns that the Chinese AI company’s technology could expose sensitive information and create security risks, according to an article from TechRepublic. The Department of Homeland Security (DHS) has ordered federal civilian agencies to remove DeepSeek products from their IT systems and prohibited purchases of the company’s technology. According to the DHS notice, the restrictions also extend to certain third-party products and services incorporating DeepSeek technology, potentially affecting federal agencies and vendors that rely on the company’s AI models. On 20 October 2026, the PHP project announced an upcoming security release addressing two critical vulnerabilities in PHP, according to an advisory posted by CERT-EU. Public reports indicated that these vulnerabilities could lead to remote code execution. The PHP team released the fixes on 21 October 2026 at 13:30 UTC, in PHP versions 8.5.12, 8.4.27, 8.3.36 and 8.2.35 [4]. Both vulnerabilities can allow unauthenticated remote code execution. Technical details are now being discussed publicly, and initial proofs of concept (PoCs) have begun to circulate. This raises the likelihood that attackers are already exploiting the vulnerabilities. CERT-EU advises organisations to patch affected assets immediately. Where that is not feasible, organisations should consider isolating internet-facing applications from public networks until a fix is applied and verified. You can also read more about the newly discovered PHP vulnerabilities here, from this article from The Guardian. (PCLinuxOS already has the patches). Google said it's rolling out improved safeguards in its Chrome browser to secure users against ClickFix attacks when Enhanced Protection is enabled, according to an article from The Hacker News. ClickFix is a popular social engineering technique in which bad actors trick users into copying and pasting malicious code directly into their computer's operating system, thereby bypassing conventional security controls. As part of these attacks, unsuspecting users who land on legitimate-but-compromised sites or click on malicious ads are redirected to phishing landing pages that display fake Cloudflare or Google reCAPTCHA verification or other non-existent errors and instruct users to copy and paste a command on the Windows Run dialog (or the Mac Terminal app) to address it. The moment a user presses the Enter key after pasting the command, it triggers a multi-stage infection chain that leads to the deployment of malware, such as information stealers or remote access trojans. In an attempt to blend in with regular activity and evade detection, the commands often make use of living-off-the-land (LotL) tools like PowerShell or cmd.exe to download next-stage payloads.  Turning off tracking on a smart TV may not stop it from communicating with tracking-related servers, according to an article from eSecurity Planet. Researchers at Northeastern University tested 12 smart TVs from 10 manufacturers and found that some continued sending network traffic associated with automatic content recognition (ACR) even after users opted out. ACR is technology that can identify what people watch on their television screens. The findings raise questions about how reliably smart TV privacy settings work. However, because much of the traffic was encrypted, researchers could not conclusively determine what information was transmitted or whether viewing histories continued to be collected. Opt-out buttons exist to give users control over whether their smart TVs collect and transmit viewing-related data. However, after running 5,943 experiments, researchers found that some TVs continued sending network traffic consistent with tracking even after users had opted out, raising questions about whether these privacy controls work as expected. Scientists today say we’re just beginning to understand the harm that the tiny bits of plastic we drink, eat and breathe are doing to the human body. But recently discovered chemical company documents dating back several decades show that industry scientists have long been aware of — and concerned about — the way microplastic particles migrate beyond the gut in animals and humans, depositing in important organs, according to an article from the LA Times. And the potential for that knowledge to affect the plastic food packaging industry. Their concern goes back to 1974 and a scientific meeting at a New York City hotel, where a German gastroenterologist presented a scientific paper that showed for the first time that ingested particles like microplastics could infiltrate the rest of the body. His presentation was largely overlooked by the government scientists in attendance but became a point of worried discussion among company scientists. A “horror story” was how one company executive described how that research was received. Google has been pushing Personal Intelligence to make its AI services useful. Instead of giving you generic answers, Gemini and Google Search can pull information from connected apps, including Gmail and Google Photos, to better understand what you’re asking and provide more relevant responses. But there’s a privacy trade-off. Google updated its privacy policy to clarify that it could use information you choose to share with certain Google services to personalize ads, according to an article from Android Authority. Given how much personal information many of us have in Gmail and Google Photos, it’s worth paying attention. Google’s privacy policy still says it doesn’t use content from Gmail, Drive, or Photos to personalize ads by default. However, an important exception now applies to users who explicitly connect that information to Google services that offer personalized advertising. So, giving Google access to your personal information for smarter recommendations could also lead to more targeted ads, depending on the service and permissions involved. |